Vulnerability Management
Prioritize remediation by real-world exploitability, not raw severity score.
Where this risk comes from
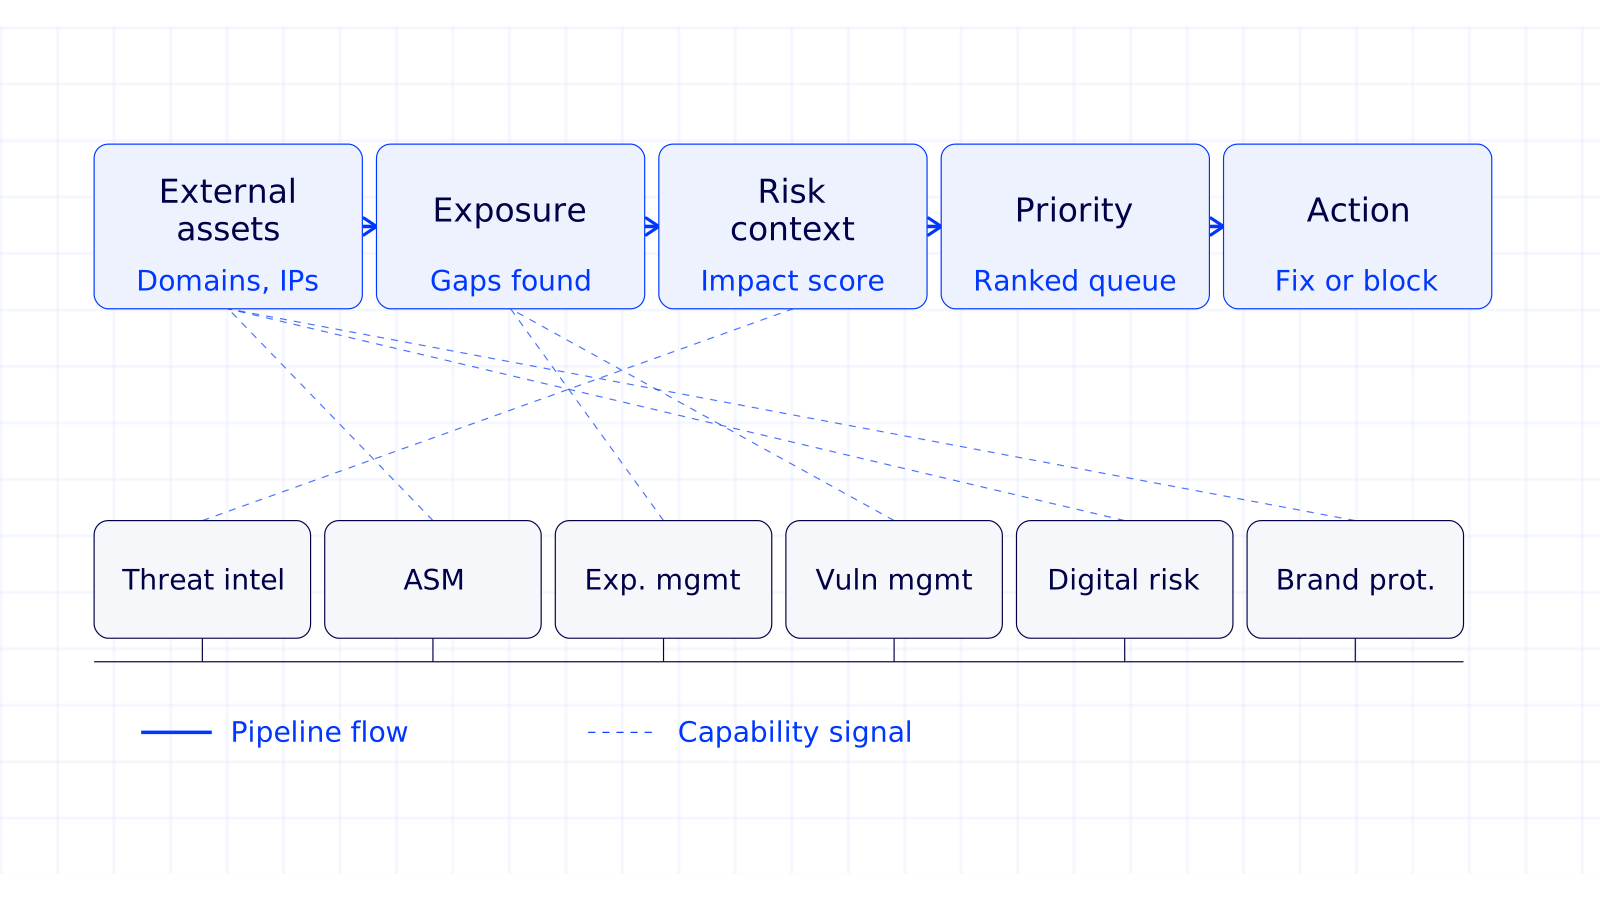
Scanning is the easy part — most programs already generate more findings than any team can remediate. The hard part is knowing which vulnerabilities actually create risk in your specific environment.
Mellivor Vulnerability Management prioritizes by exploitability and business context, not raw CVSS score, so remediation effort goes where it actually reduces risk.
What enterprises are up against
- Scan results outpacing the team's capacity to remediate
- Prioritization based on severity score alone, ignoring real-world exploitability
- Patch cycles that lag behind active exploitation timelines
- No clear ownership for remediation across IT and application teams
What's actually at stake
The gap between 'vulnerable' and 'actually exploitable in your environment' is where most remediation effort is wasted. Closing that gap is often the single biggest efficiency gain a security program can make.
Unpatched, internet-facing vulnerabilities remain one of the most common initial access vectors in real breaches — the risk is well understood, but rarely managed with the urgency it deserves.
The Mellivor approach
- Continuous scanning across cloud, on-premises, and application layers
- Risk-based prioritization weighted by exploitability and asset criticality
- Automated ticketing and ownership routing to close the remediation loop
- Reporting that shows real risk reduction over time, not just finding counts
Technology categories that support this solution
Cloud & Infrastructure
Cloud security posture, workload protection, and infrastructure monitoring technologies.
Go deeper
Mellivor's platform is backed by teams who design, deploy, and run it alongside you.
See Vulnerability Management in action
Request a demo scoped to this solution and your environment.