XDR
Correlate signal across endpoint, network, identity, and cloud into one incident view.
Where this risk comes from
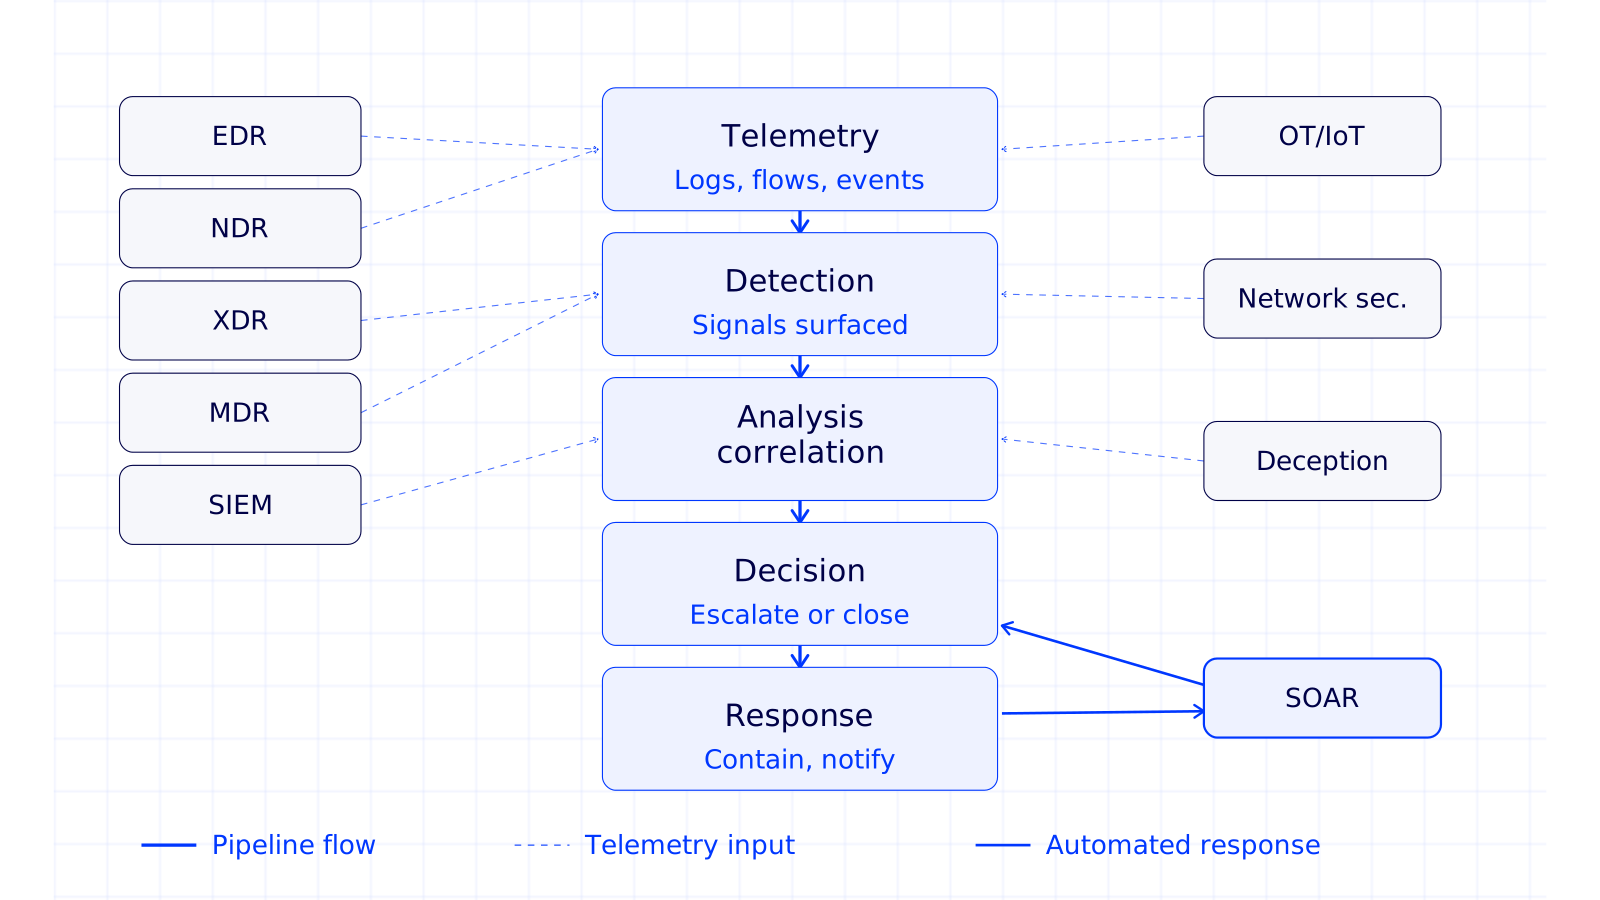
Extended Detection and Response correlates signal across endpoint, network, identity, and cloud instead of leaving analysts to manually piece together fragments from separate consoles.
Mellivor XDR is the correlation layer that ties Behind24's detection sources together into a single, prioritized incident view.
What enterprises are up against
- Security signal scattered across a dozen disconnected tools and consoles
- Analysts manually correlating alerts that should already be connected
- Slower containment because the full attack story isn't visible in one place
- Tool sprawl increasing cost without improving detection outcomes
What's actually at stake
The average enterprise SOC juggles a dozen or more security tools, each with its own alerts. XDR exists because the real story of an attack is almost always spread across several of them at once.
Faster correlation directly translates into faster containment — the time analysts spend manually connecting alerts is time an active attacker spends moving deeper.
The Mellivor approach
- Correlation of endpoint, network, identity, and cloud signal into one incident view
- Automated prioritization based on the full attack chain, not isolated alerts
- Native integration with existing tools rather than forcing a rip-and-replace
- Unified investigation workflow inside Mellivor One
Technology categories that support this solution
Detection & Response
SIEM, XDR, and threat detection technologies integrated into Behind24.
Go deeper
Mellivor's platform is backed by teams who design, deploy, and run it alongside you.