Where this risk comes from
Security Information and Event Management is still the backbone of most compliance and detection programs — the challenge has always been keeping it tuned, current, and actually useful rather than a log archive nobody queries.
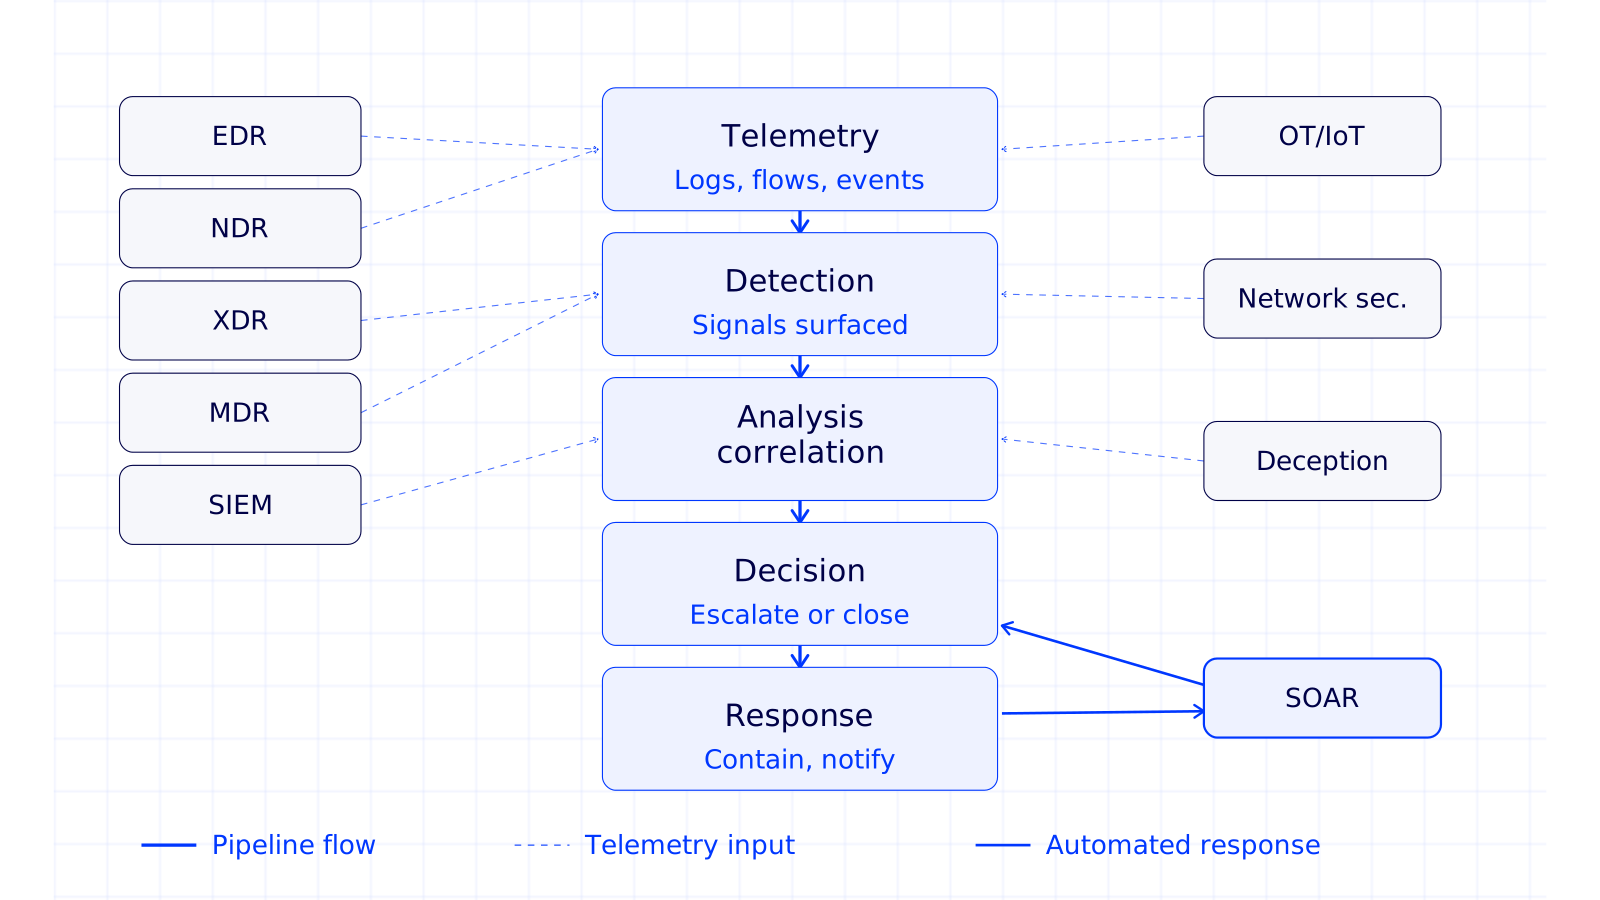
Mellivor's managed SIEM keeps detection content current and correlates log data with the same intelligence feeding Behind24.
What enterprises are up against
- Detection rules that go stale as the environment and threat landscape change
- Alert volume too high for the team to triage effectively
- Log sources onboarded inconsistently, leaving blind spots
- SIEM treated as a compliance checkbox rather than an active detection tool
What's actually at stake
A SIEM full of untuned rules generates so many false positives that real alerts get lost in the noise — which means an under-managed SIEM can create a false sense of security rather than actual protection.
Compliance frameworks routinely require centralized logging and monitoring; a well-run SIEM often satisfies audit requirements and real detection needs at the same time.
The Mellivor approach
- Managed onboarding and normalization of log sources across the environment
- Continuously updated detection content informed by current threat intelligence
- Tuning to reduce false positives without losing real signal
- Direct handoff into Behind24 for triage and response
Go deeper
Mellivor's platform is backed by teams who design, deploy, and run it alongside you.