OT / IoT Security
Visibility and protection built around the constraints of operational technology.
Where this risk comes from
Operational technology and IoT devices were built for uptime and reliability, not security — many can't run agents, can't be patched during operation, and were never meant to be internet-connected in the first place.
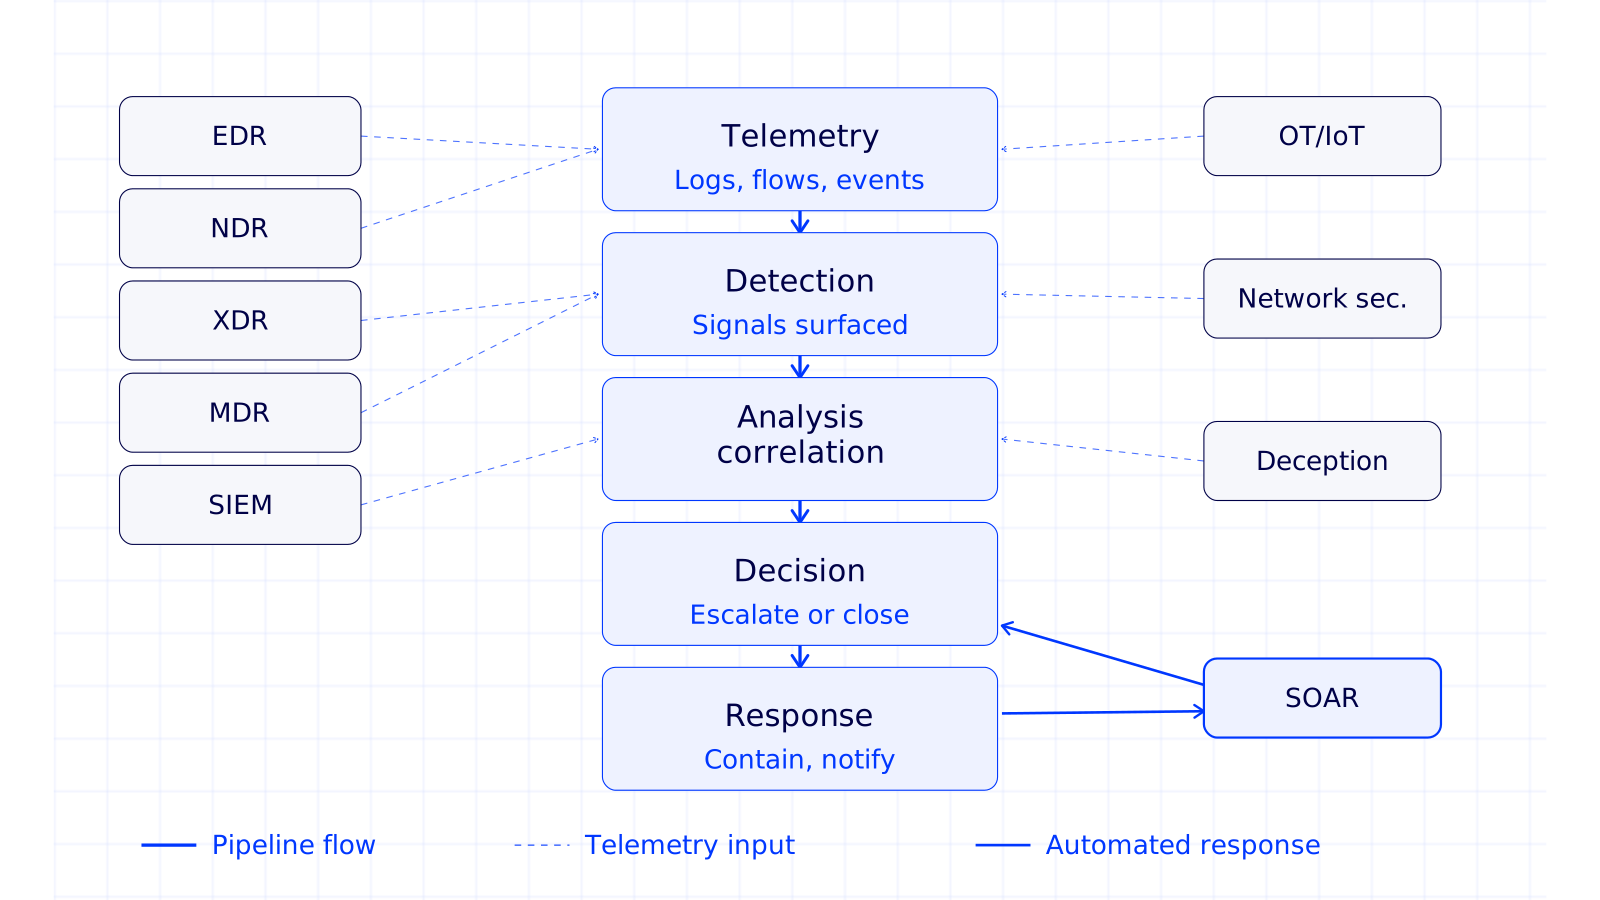
Mellivor OT/IoT Security provides visibility and protection designed around those constraints, not a repurposed IT security playbook.
What enterprises are up against
- Devices that can't support traditional agents or frequent patching
- IT and OT networks converging faster than security controls can adapt
- Limited visibility into device inventory and communication patterns
- Legacy protocols with no built-in authentication or encryption
What's actually at stake
An incident in OT doesn't just risk data — it can risk physical safety and operational continuity, which changes the risk calculus and the acceptable response time entirely.
These environments are also frequently the least visible part of the enterprise, making them an attractive path for attackers looking to move from IT into systems that matter physically.
The Mellivor approach
- Passive discovery and monitoring that doesn't disrupt operational systems
- Segmentation between IT and OT environments to limit blast radius
- Protocol-aware detection tuned to industrial and IoT communication patterns
- Risk assessments that account for safety and uptime, not just data
Go deeper
Mellivor's platform is backed by teams who design, deploy, and run it alongside you.
See OT / IoT Security in action
Request a demo scoped to this solution and your environment.