NDR
Catch lateral movement and anomalous behavior traditional tools miss.
Where this risk comes from
Network Detection and Response watches traffic patterns for the kind of anomalous behavior that endpoint and perimeter tools miss — especially once an attacker is already inside and moving laterally.
Mellivor NDR analyzes network behavior continuously, flagging the traffic patterns that don't match how your environment normally operates.
What enterprises are up against
- Lateral movement that bypasses endpoint detection entirely
- Unmanaged and IoT devices that can't run traditional agents
- Encrypted traffic limiting visibility into actual payloads
- East-west traffic inside the network going largely unmonitored
What's actually at stake
Attackers who evade endpoint detection still have to move across the network to reach anything valuable — which makes network behavior one of the few signals that's genuinely hard to hide from.
NDR is also one of the few controls effective against unmanaged and IoT devices that can't run traditional endpoint agents at all.
The Mellivor approach
- Continuous behavioral analysis of east-west and north-south traffic
- Detection tuned to your environment's actual traffic baseline, not generic signatures
- Coverage for unmanaged and IoT devices without requiring agents
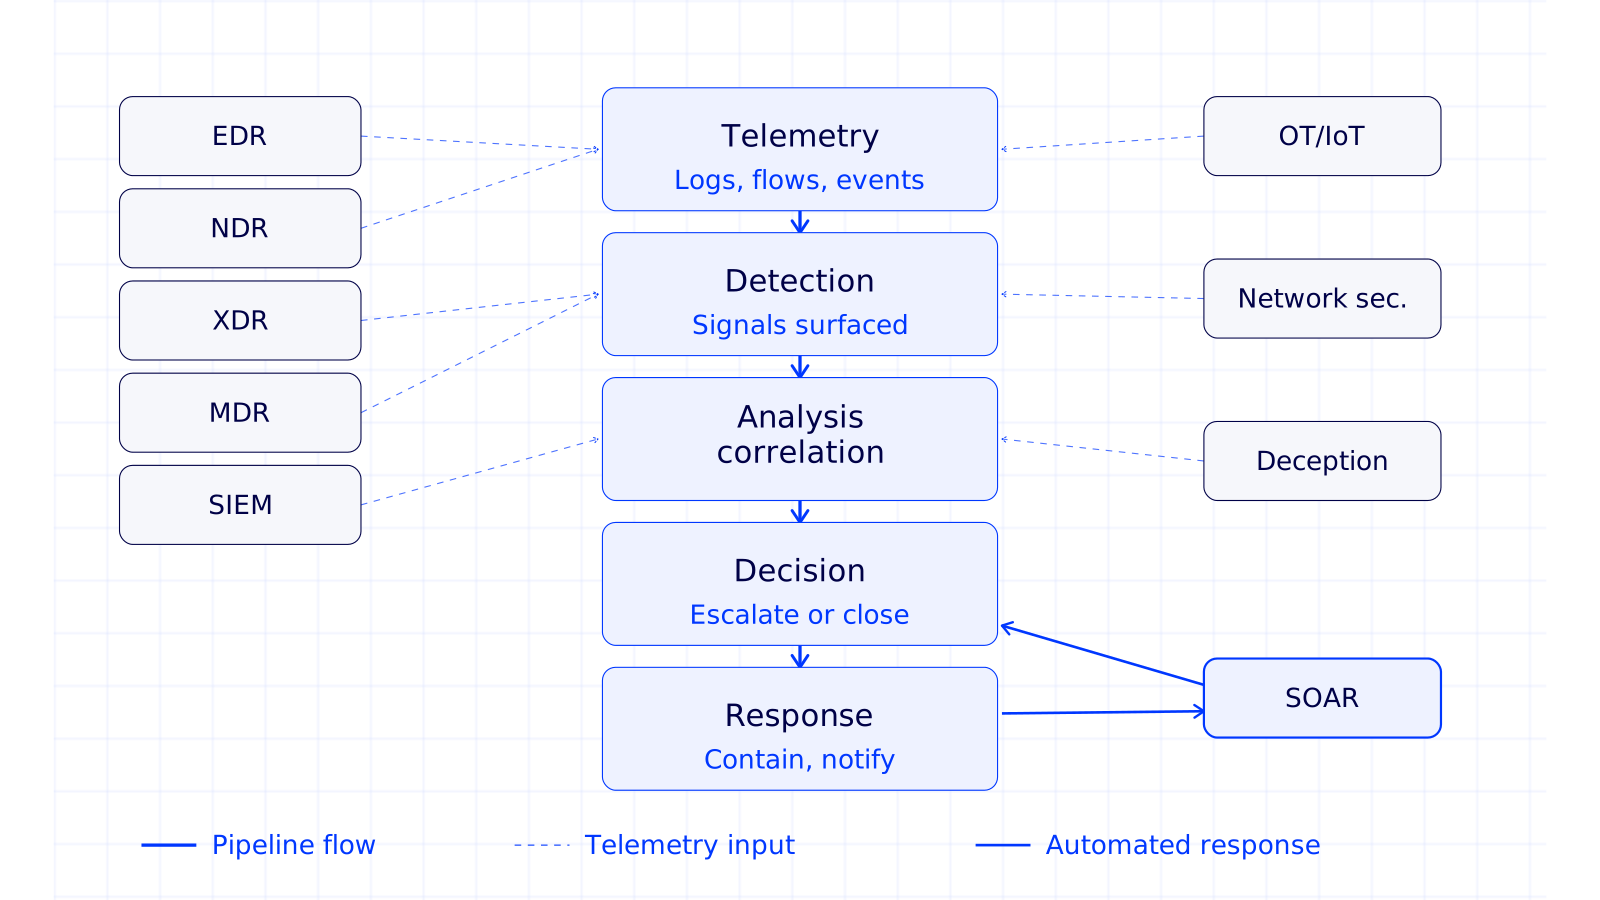
- Correlation with endpoint and identity signal through Behind24
Technology categories that support this solution
Detection & Response
SIEM, XDR, and threat detection technologies integrated into Behind24.
Go deeper
Mellivor's platform is backed by teams who design, deploy, and run it alongside you.