MDR
24/7 detection and response, delivered through Behind24, without building a SOC from scratch.
Where this risk comes from
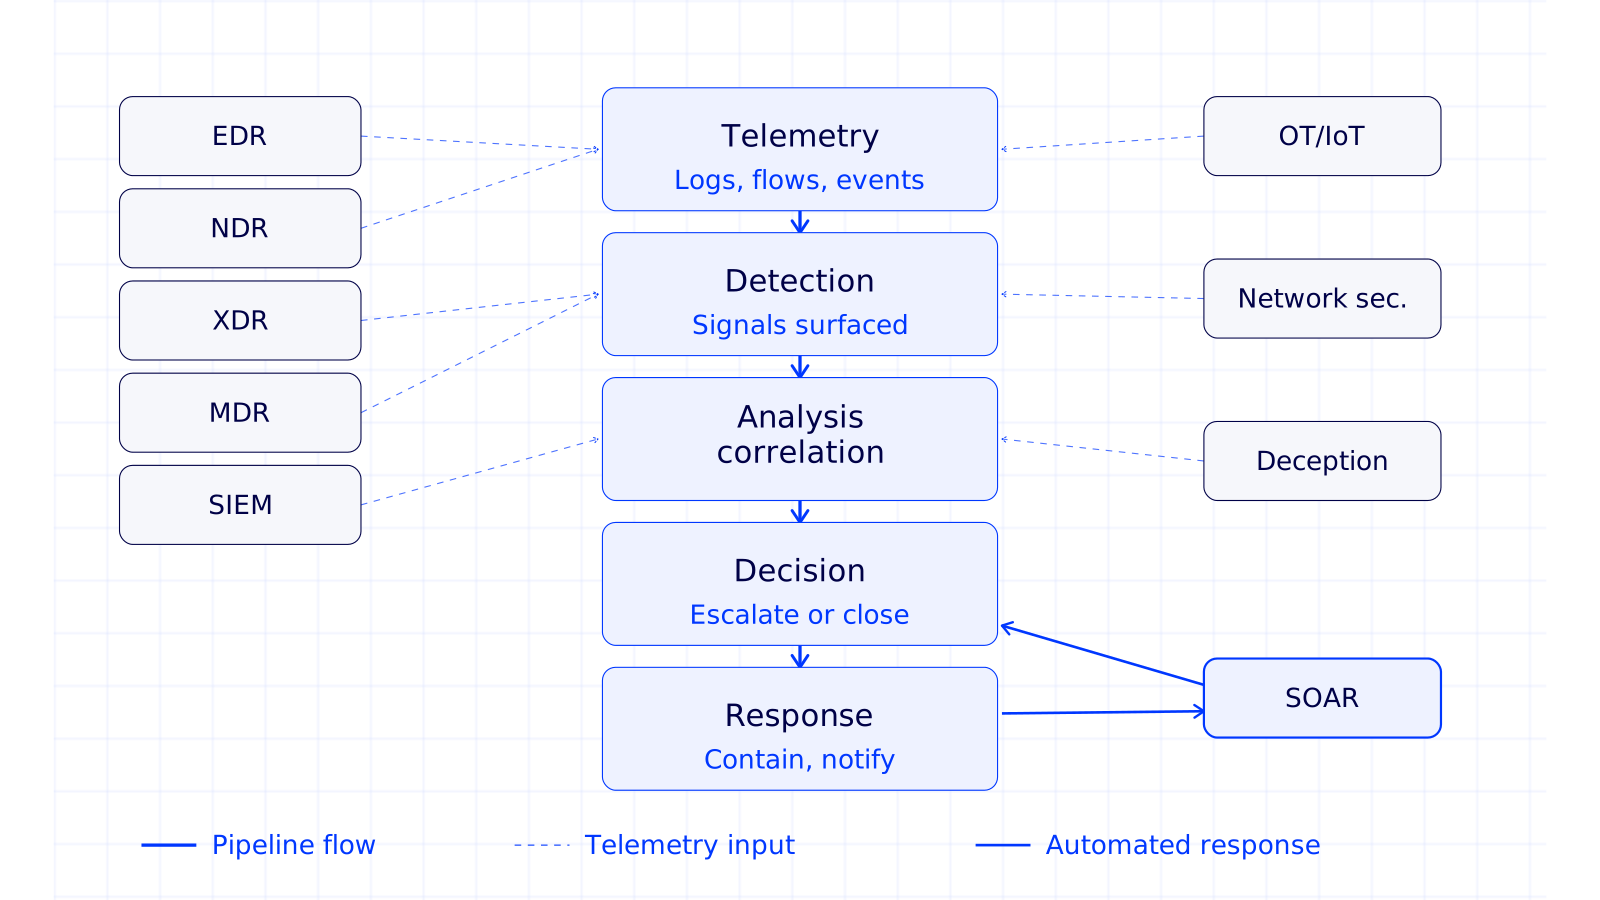
Managed Detection and Response gives you a 24/7 SOC without having to build, staff, and retain one yourself — one of the hardest and most expensive parts of a modern security program.
Mellivor MDR, delivered through Behind24, combines continuous monitoring with analysts who actually respond, not just forward alerts back to your team.
What enterprises are up against
- No practical way to staff a 24/7 SOC with in-house talent
- Alert volume outpacing the internal team's ability to triage
- Detection without the follow-through to actually contain an incident
- Skills gaps in emerging attack techniques and threat actor behavior
What's actually at stake
Attacks don't happen on business hours. Without continuous coverage, detection and response can be significantly delayed.
The security talent shortage makes round-the-clock in-house SOC coverage impractical for most organizations outside the largest enterprises — MDR is often the only realistic path to real 24/7 coverage.
The Mellivor approach
- 24/7 monitoring and triage delivered through Behind24
- Analysts empowered to take direct containment action, not just alert
- Regular threat hunting beyond automated detection rules
- Transparent reporting so your team always knows what happened and why
Technology categories that support this solution
Detection & Response
SIEM, XDR, and threat detection technologies integrated into Behind24.
Go deeper
Mellivor's platform is backed by teams who design, deploy, and run it alongside you.