EDR
Detect and contain compromised endpoints before an incident spreads.
Where this risk comes from
Endpoint Detection and Response is the last line of defense once an attacker has a foothold on a device — and increasingly the first place sophisticated attacks are actually caught.
Mellivor EDR combines behavioral detection with the response actions needed to contain a compromised endpoint immediately, not after a ticket is filed.
What enterprises are up against
- Fileless and living-off-the-land techniques that evade signature-based tools
- Endpoints that go unmonitored outside the managed device fleet
- Detection without the ability to immediately isolate a compromised device
- Alert fatigue from endpoint tools tuned too loosely or too strictly
What's actually at stake
Ransomware and most modern intrusions eventually touch an endpoint — the question isn't whether that happens, it's whether it's caught in the first minutes or discovered days later.
The speed of containment at the endpoint often determines whether an incident stays isolated to one machine or spreads across the network.
The Mellivor approach
- Behavioral detection tuned to living-off-the-land and fileless techniques
- One-click isolation and remediation actions available directly to responders
- Coverage extended to unmanaged and BYOD endpoints where possible
- Continuous tuning informed by Behind24 threat intelligence
Technology categories that support this solution
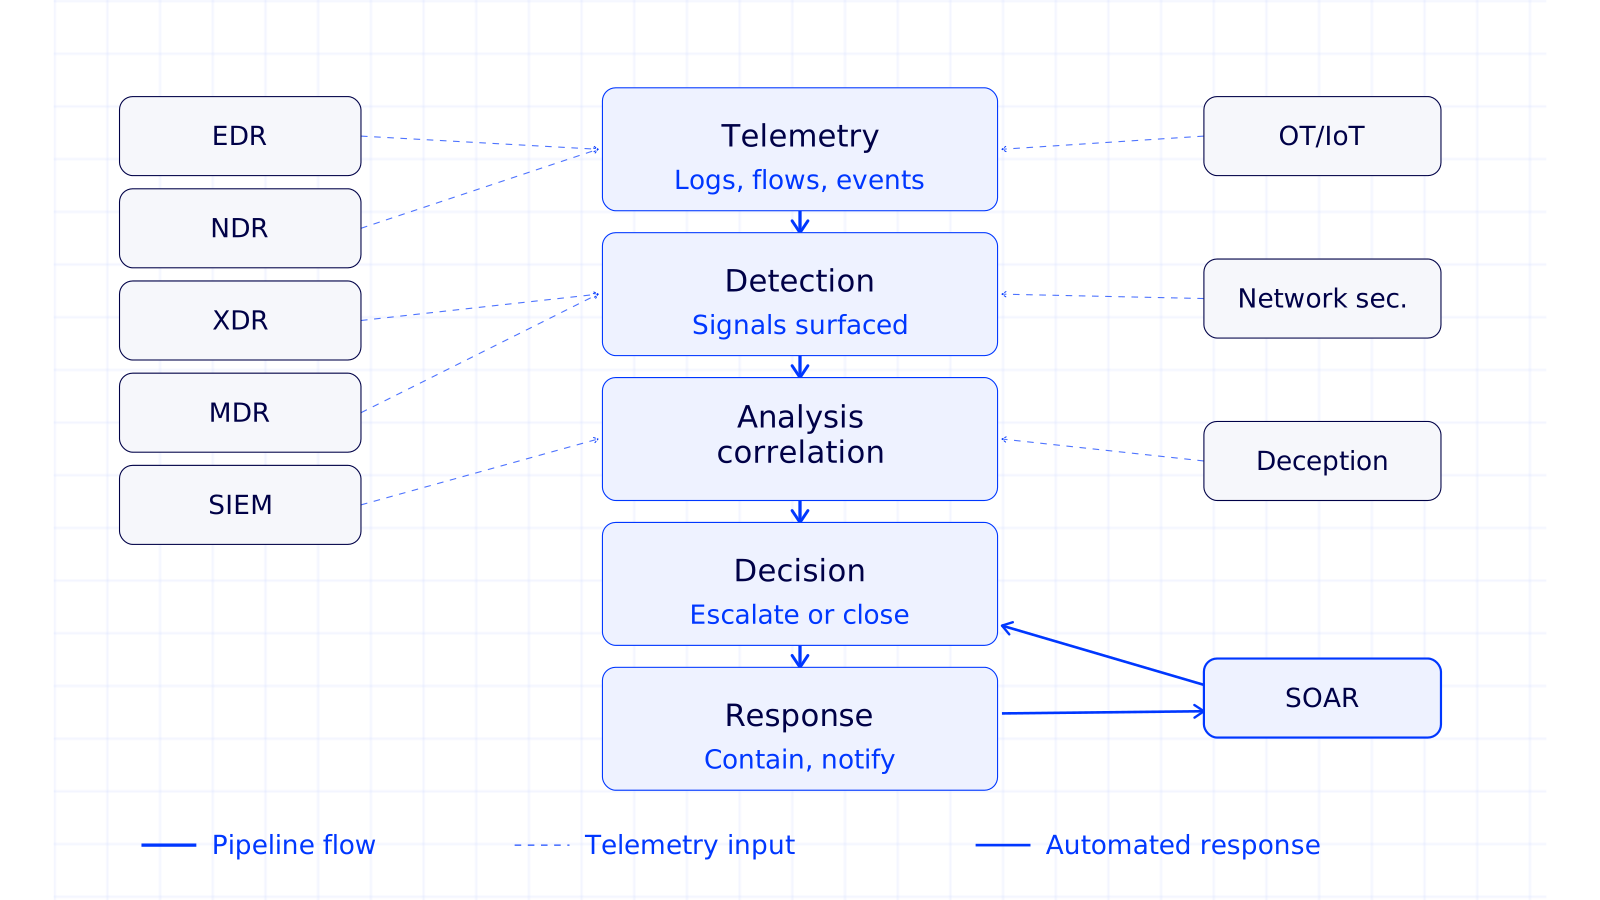
Detection & Response
SIEM, XDR, and threat detection technologies integrated into Behind24.
Go deeper
Mellivor's platform is backed by teams who design, deploy, and run it alongside you.